games
Capcom Suspends Street Fighter V Sales as PHP Security Work Continues

 Add Gaming.net to your preferred sources on Google
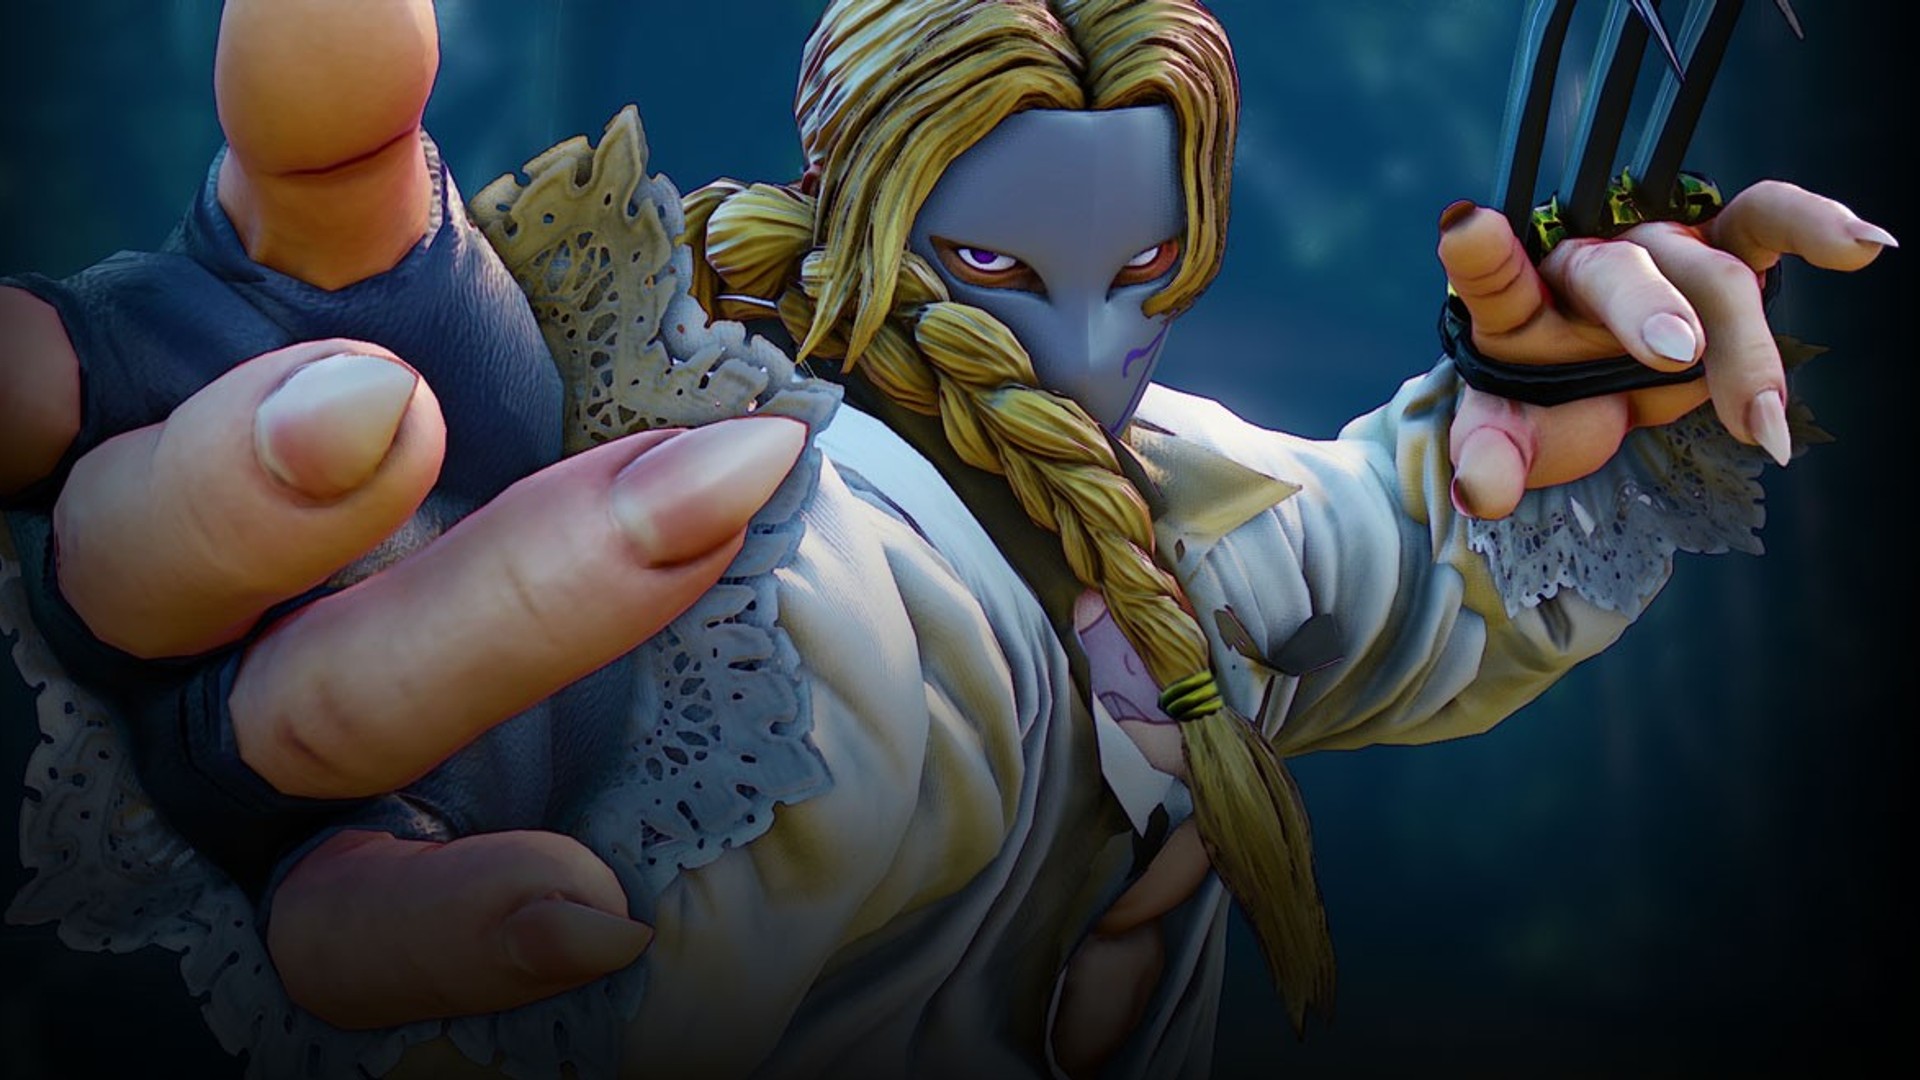
Capcom said on October 27, 2026 that online functionality in the PlayStation 4 and Steam versions of Street Fighter V remains unavailable as the company works to strengthen security tied to the PHP programming language used in those versions, and that sales on the PlayStation Store and Steam will be suspended in stages until the fix has been completed.
In a notice posted to the official Street Fighter account, the publisher said emergency maintenance is underway to address the issue. The notice said offline content remains playable, and Capcom apologized for the inconvenience.
The suspension is already visible on Valve’s storefront. The Street Fighter V page on Steam carries the notice: “Street Fighter V is no longer available on the Steam store.”
The game’s official Capcom Fighters Network website, CAPCOM:Shadaloo C.R.I., is showing a maintenance page that reads: “We are currently undergoing maintenance. Please wait a moment.”
Emergency Maintenance Notice Posted October 23
Capcom posted a Notice of Emergency Maintenance on the Street Fighter V Steam news page on October 23, 2026, at 6:05 AM EDT. In it, the company said that, due to security enhancements related to the PHP programming language, content using online features was unavailable, offline-playable content remained available, and emergency maintenance was underway to resolve the issue.
PHP Project Patched Two Critical Vulnerabilities
On October 20, 2026, the PHP security team gave advance notice of a security release scheduled for October 21, 2026 at 14:00 UTC. The team said the release would address two critical vulnerabilities, both rated 9.2 under the CVSS v4.0 severity scale, and reserved the right to release it earlier if details became public or evidence of active exploitation appeared in the wild.
The project released PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on October 21, 2026. The releases fix CVE-2026-109618 and CVE-2026-109619, two critical vulnerabilities that can allow unauthenticated remote code execution, and the PHP team urged all users to update immediately, stating there are no complete mitigations.
According to the project’s security advisory, all PHP installations serving web requests are at risk, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. The team considers the risk highest for mod_php, citing a demonstrated exploit in which an unauthenticated request can trigger the attack before any application code runs.
The GitHub advisory for CVE-2026-109618, titled RCE via OOM corruption, describes a flaw in which an out-of-memory error can abort a request while its internal data is only partially initialized, leaving shutdown routines to process invalid state. The PHP security team said it validated complete remote code execution over HTTP against mod_php with default input and memory limits. Versions below 8.2.35, 8.3.36, 8.4.27 and 8.5.12 are affected.
The advisory for CVE-2026-109619, RCE via stale global state, describes internal state owned by one request that survives after the memory behind it has been freed, so a later request handled by the same worker can act on the stale state before normal initialization resets it, producing a use-after-free. The team said remote code execution was validated against mod_php and FPM through a session upload progress path, and that exploitation requires the producing and consuming requests to reach the same worker.
The PHP project published further advisories after the October 21 releases. On October 23, 2026, it recommended setting session.upload_progress.enabled=0 until the next regular bugfix release and said it will publish a full advisory for CVE-2026-115560 with that release, describing the underlying issue as requiring an unusual combination of configuration and application code. On October 26, 2026, the project announced updated Windows builds, PHP 8.5.12-1, 8.4.27-1, 8.3.36-1 and 8.2.35-1, which bundle Brotli 1.2.1 to fix CVE-2026-111497, an out-of-bounds write in Brotli decompression that can be reached through the cURL extension when automatic HTTP response decompression is enabled. That option is disabled by default in cURL, though applications and HTTP client libraries can enable it, the project said.
For older branches, the PHP security team provided minimal source backports covering PHP 7.4, 8.0 and 8.1; PHP 8.1 and older no longer receive updates from the project. PHP 8.2 reaches end of life on December 31, 2026, and will receive no further security fixes after that date.
Street Fighter V Background
Street Fighter V was released on February 15, 2016. Developed and published by CAPCOM Co., Ltd., the fighting game was released for PlayStation 4 and PC, and the Steam version features cross-platform play between PlayStation 4 and Steam players.
According to Capcom’s official site, Street Fighter V: Champion Edition includes all content from the original release and Street Fighter V: Arcade Edition, excluding Fighting Chance costumes, brand collaboration costumes and Capcom Pro Tour DLC, for a total of 40 characters, 34 stages and over 200 costumes. All game mode additions and balance updates are free for owners of any Street Fighter V version, and all DLC characters can be earned free of charge through in-game challenges that award Fight Money, the game’s currency, according to Capcom.